The NIST Cybersecurity Framework is a set of guidelines created by the National Institute of Standards and Technology (NIST) that businesses can use to strengthen their cybersecurity from the ground up. The framework was developed in response to the rising number of cyberattacks on businesses across the United States, and it has since become one of the most widely adopted security standards in the world.

It includes best practices businesses can follow to protect their data, networks, and systems from cyberattacks. In this blog post, we’ll discuss what the NIST Cybersecurity Framework is, why businesses need to implement it, and how they can get started.
What Is the NIST Cybersecurity Framework?
NIST is a federal agency that creates standards and guidelines to help organizations improve their cybersecurity. The NIST Cybersecurity Framework was created in response to the ever-rising number of cyberattacks on businesses across the country and the globe.
At its core, the framework is organized around a handful of high-level functions that describe the full lifecycle of managing cyber risk: Identify, Protect, Detect, Respond, and Recover — and, in the latest Version 2.0 released in 2024, a sixth function, Govern, which emphasizes leadership accountability and risk management strategy. Together, these functions give businesses of any size a common language for understanding where they stand and what to improve.
The NIST Cybersecurity Framework can be used as a starting guide for how businesses should approach cybersecurity and data protection. That said, it’s best to protect your sensitive data not only with these guidelines but also with additional security measures from professional cybersecurity providers.
Why Is the NIST Cybersecurity Framework Important for Businesses?
The NIST Cybersecurity Framework is important for businesses because it provides flexible, up-to-date guidance for protecting data from cyberattacks. In today’s world, data is one of the most valuable assets a business owns, and it’s under constant threat.
Cyberattacks are becoming more common and increasingly expensive. The average cost of a data breach has climbed into the millions of dollars, and that figure rises nearly every year. By implementing the NIST Cybersecurity Framework, companies can systematically improve and invest in their defenses, reducing both the likelihood and the impact of an attack.
By following the framework’s guidance, businesses can also avoid many of the fines and penalties that regulatory agencies may impose after a breach. Additionally, the NIST Cybersecurity Framework helps businesses align with and comply with various laws and regulations, such as the General Data Protection Regulation (GDPR) and HIPAA — making it a valuable foundation for organizations in regulated industries like healthcare and finance.
How Can Businesses Implement the NIST Cybersecurity Framework?
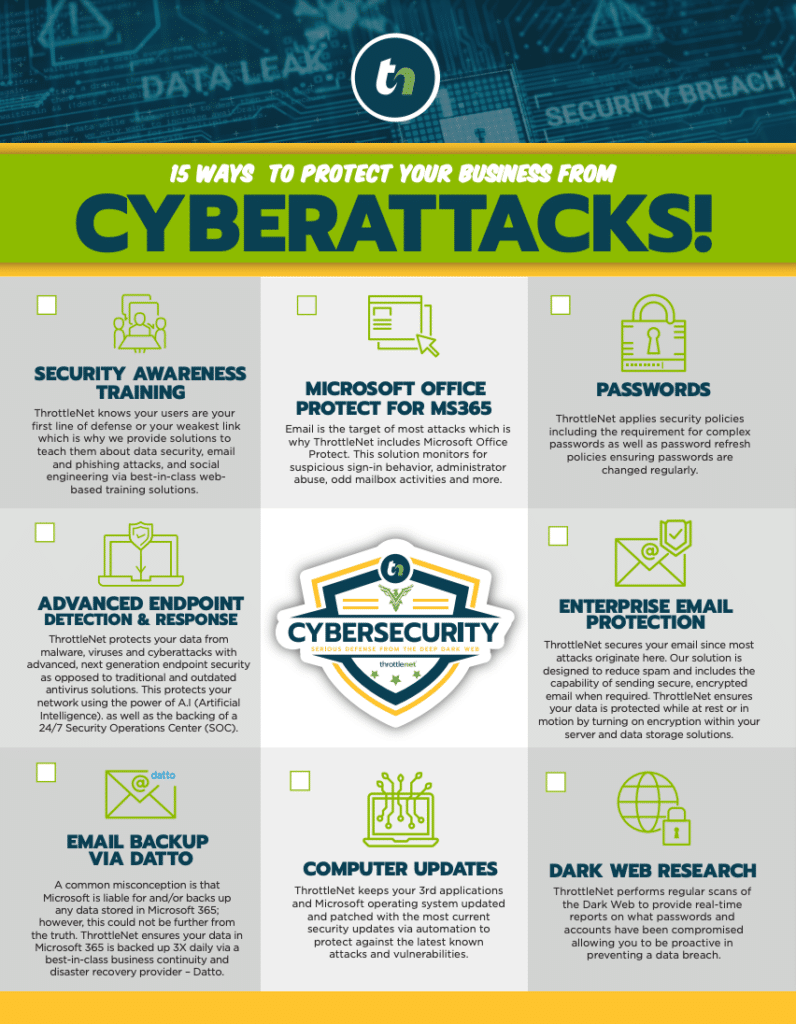
Businesses can implement the NIST Cybersecurity Framework by following the best practices it outlines. These include conducting a risk assessment to understand your current security posture, creating a formal cybersecurity plan, training employees to recognize threats, and putting technical security controls in place such as firewalls, multi-factor authentication, and continuous monitoring.
A practical way to begin is to work through the framework’s functions in order: identify your most critical assets and risks, protect them with appropriate safeguards, build the ability to detect incidents quickly, prepare a clear plan to respond, and ensure you can recover operations with minimal disruption. Because the framework is designed to be flexible, you can scale each step to fit your business’s size, budget, and industry.
Businesses should also consider working with a professional cybersecurity company to help implement the NIST Cybersecurity Framework. Cybersecurity is a complex, fast-moving field, and partnering with experts ensures you’re taking all the necessary steps to protect your data rather than leaving gaps an attacker could exploit.
You Can Get Started Today
To summarize, the NIST Cybersecurity Framework is a guideline created by the National Institute of Standards and Technology that businesses can use to improve their cybersecurity. It includes best practices companies can follow to keep sensitive information secure and out of the hands of hackers.
The NIST Cybersecurity Framework is especially valuable because it’s a continually updated, living document — it evolves alongside the threat landscape to guide you on the latest best practices and protect sensitive information from attackers.
How ThrottleNet Can Help
If you have any questions about the NIST Cybersecurity Framework or how to implement it, reach out to one of our IT experts at ThrottleNet. That’s the first step toward incorporating the NIST Cybersecurity Framework into your security structure. We’re in the business of helping companies protect their data from cybersecurity threats of all kinds, and we’d be happy to assist you.